Hello everyone,
Following three weeks of pre-production testing, I am proud to announce the release of NGX Ops 1.1.0, alongside NGX Ops Intelligence, a new platform designed to centralise and analyse security alerts.
Yes, the project is changing its name yet again! After Nginx Control, it’s now NGX Ops. This time, the change is primarily a strategic decision: I want to ensure the project’s long-term future and avoid any confusion with F5 and the products associated with the NGINX brand. The aim now is to build on a sustainable foundation, with an identity unique to the project.
NGX Ops 1.1.0: a release packed with new features
This release is not merely a name change. It introduces a number of technical improvements, covering security, administration, automation and the user experience.
A more powerful analysis engine
One of the major developments is the rewrite of the Nginx Agent Analyzer in Go. This work brings with it a number of improvements:
- Integration of an internal IP blocklist based on the scanning rules.
- Option to ignore certain HTTP status codes in order to reduce the load on the agent, particularly for
444responses. - Displaying the information learnt by the analysis engine.
- Option to test the Nginx configuration in a short-lived container.
The aim is to make the analysis more effective and to make better use of the information collected in order to enhance the security of Nginx instances.
Enhanced security
Version 1.1.0 also introduces several features designed to protect exposed services:
- Emulated WAF: using detection rules to identify suspicious behaviour, without necessarily requiring a traditional WAF.
- HTTP Challenge: support for the built-in engine and Anubis.
- Synchronising Let’s Encrypt certificates across multiple Nginx instances.
The emulated WAF forms part of a complementary approach: it enables behaviour matching security rules to be detected and utilised in the analysis. However, it does not replace a full-featured WAF capable of inspecting the content of requests, particularly the bodies of HTTP requests.
Simpler administration
A number of changes also make day-to-day administration easier:
- Registering an Nginx agent directly from the dashboard.
- New page for managing containers linked to NGX Ops.
- Redesign of the scheduled tasks system, using SQLite storage instead of YAML files.
- Overhaul of the notification system, which has also been migrated to SQLite.
- New global search in the interface header.
- Search directly within the configuration files.
- Improvements to the configuration page.
- You can configure the User-Agent used for HTTP requests via
HTTP_USER_AGENT.
Finally, integration with NGX Ops Intelligence now makes it possible to extend analytical capabilities beyond a single instance.
NGX Ops Intelligence: moving from alerts to insights
This is the other major new feature in this version.
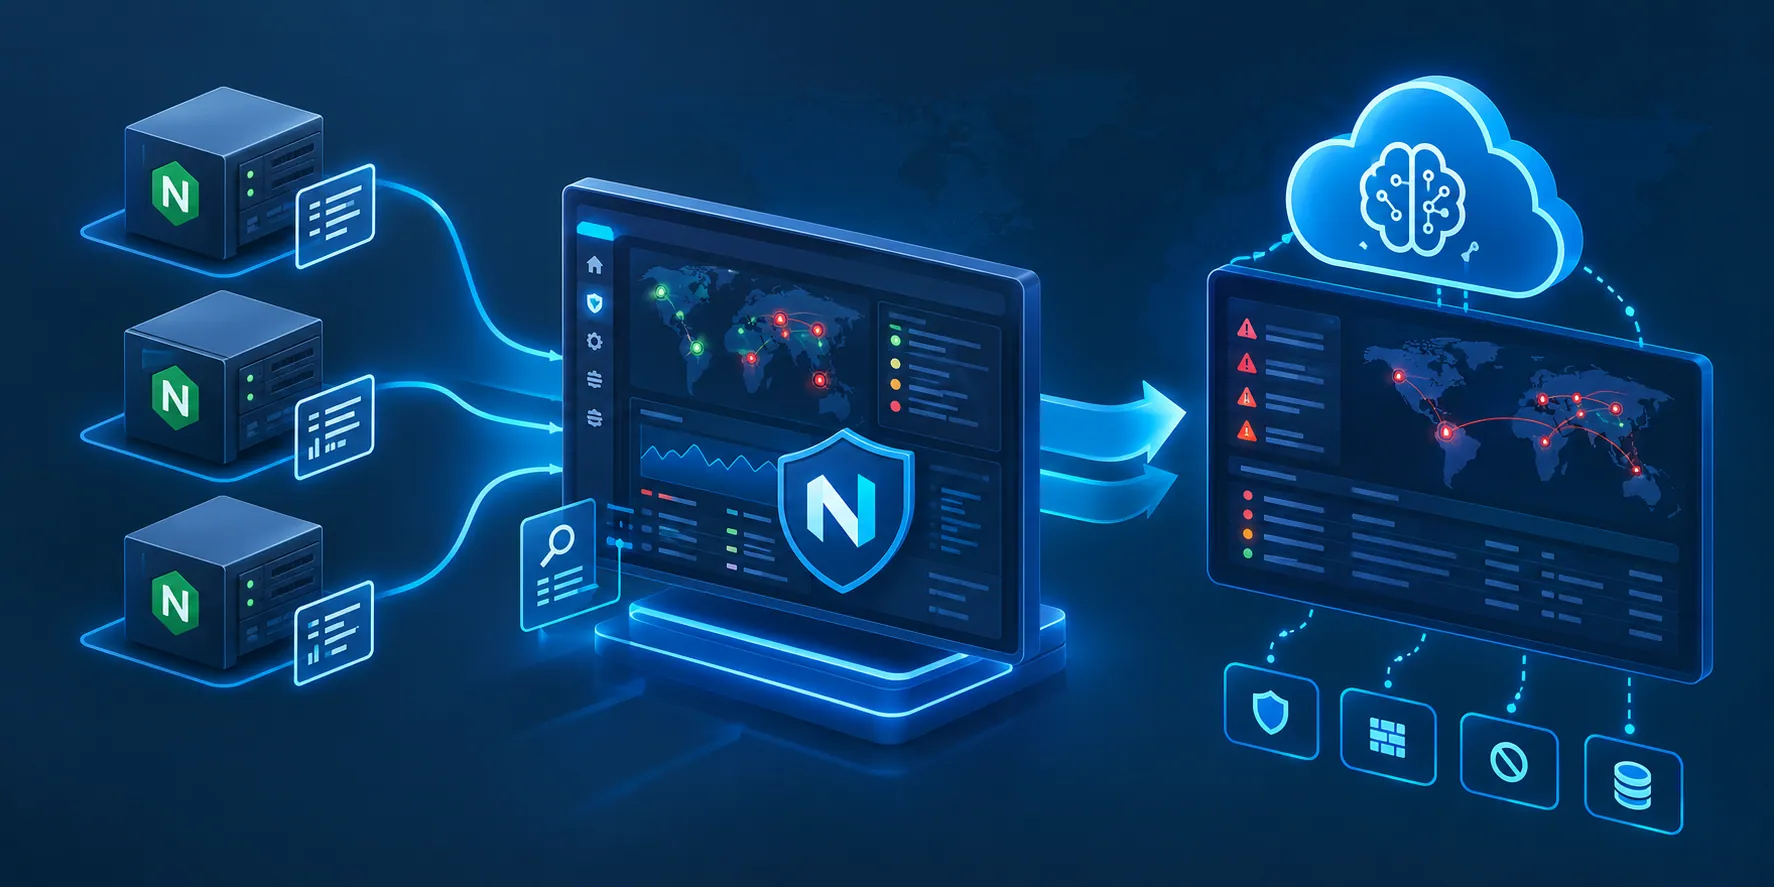
NGX Ops Intelligence is a centralised platform that collects analysis rule reports and events from the emulated WAF originating from participating NGX Ops instances.
The aim is to pool information that is useful for detecting malicious IP addresses and to facilitate its use within the organisation’s infrastructure.
But the value of this goes beyond simply producing a list of IP addresses to block.
An address appearing on a blocklist is only useful if you understand why it is there. NGX Ops Intelligence therefore aims to retain the context of detections: which rule was triggered, what behaviour was observed, and why the IP address was deemed suspicious.
This approach provides a better understanding of blocking decisions, facilitates the analysis of events and gradually improves the protection of exposed services.
Data reporting to NGX Ops Intelligence is optional and disabled by default. Each administrator is therefore free to choose whether they wish to participate in this centralisation.
The aim is to develop NGX Ops into a coherent system comprising Nginx instances capable of analysing their own traffic, local protection and a central platform that enables the organisation to make the most of the information reported up the chain.
The documentation is starting to take shape
Work is also continuing on the project’s documentation. This will be essential for helping users get to grips with the system, explaining the various security mechanisms and supporting deployments.
You can now access the various resources for the project:
- Official website: https://ngx-ops.net
- Documentation: https://docs.ngx-ops.net
- NGX Ops Intelligence: https://intelligence.ngx-ops.net/
- Source code: https://forge.rdr-it.com/ngx-ops/ngx-ops
What now?
Version 1.1.0 marks an important milestone for NGX Ops. The project is evolving from a tool for managing and analysing Nginx configurations into a solution that combines administration, detection and optional sharing of security intelligence.
There is still work to be done, particularly in terms of expanding the documentation, improving the analysis mechanisms and further developing NGX Ops Intelligence.
As always, we welcome your feedback, suggestions and contributions.
What do you think of this new version and the idea of centralising security detections across multiple Nginx instances?